Agentic AI can transform how organizations operate and grow but only when they can trust it with meaningful work. Join security practitioners and AI builders to explore what it takes to test AI deployments, control the actions they can take, and respond when things go wrong.
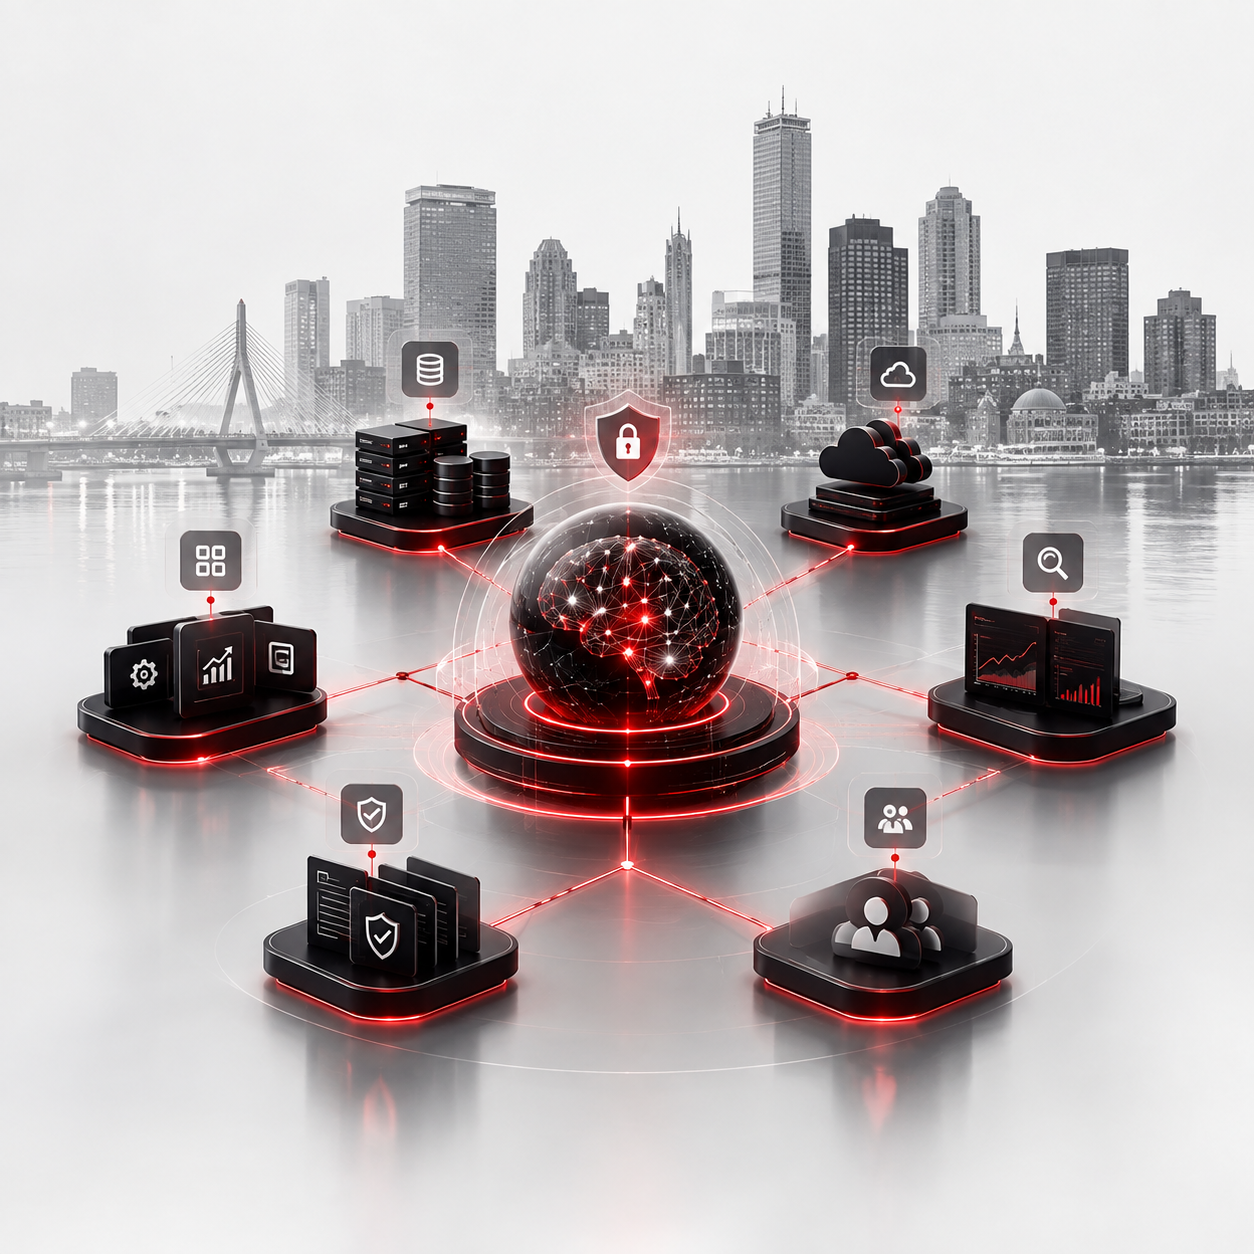
AI systems can now retrieve internal information, interact with business tools, recommend decisions, and increasingly act on behalf of people.
That creates a new operational question: How do organizations give AI meaningful responsibility without losing control?
The answer requires more than model security alone. It requires a trust layer across how AI is deployed, monitored, tested, governed, and stopped when necessary. The Trust Layer of AI Operations brings these perspectives together in one practical conversation.

Can we give AI meaningful responsibility while keeping humans accountable? Explore permissions, human approval, escalation, oversight, and recovery for systems that can take action.
If something goes wrong, can we see it, understand it, and respond? Explore how security teams can recognize suspicious activity, investigate what happened, and coordinate an effective response across AI systems and connected tools.
How could the deployment be manipulated? Examine how adversarial testing can expose weaknesses across AI inputs, retrieval sources, models, and connected tools—and how those findings can inform stronger controls.
This conversation is designed for people responsible for building, securing, deploying, or governing AI in real-world environments.
Security Leaders: Evaluating how existing security operations need to adapt to AI deployments.
AI & Platform Engineers: Building applications and agentic workflows that interact with enterprise systems.
Technology Decision-Makers: Assessing when and how AI can safely move from experimentation into production.
Founders & AI Builders: Deploying AI into meaningful business processes and determining what safeguards are needed as access expands.

Ahrar Naqvi
CEO, Ebryx
Ahrar leads Ebryx, a global cybersecurity and secure engineering company serving organizations across North America, the Middle East, and Europe. His work spans managed security, advanced R&D, and Zero Trust for critical infrastructure. He previously held senior Engineering roles at Palmchip, Veraz Networks, and Oracle and holds a master's degree in electrical engineering from Stanford University.
View linkedin ProfileWhat is your team trying to decide before putting an AI application into production or before giving an existing agent additional access?
Bring that question to the conversation.
You can share a non-confidential question when you register, and contributors will use audience questions to ground the discussion in real deployment challenges.

The questions around trustworthy AI don't end when the session does. Connect with peers working through practical security decisions across AI applications, enterprise systems, and emerging agentic workflows. Participation in the ongoing SecureNow community is optional and separate from event registration.
Explore what it takes to build the trust layer around your AI operations
Your journey to better security doesn’t have to be complicated. We make it simple to get started. Whether you have a question, need a quote, or want expert advice just reach out.